CHAINGUARD CHECKS
CI for faster green PRs without sacrificing security
Stop waiting on central build queues. Agents and developers run identical checks pre-commit or through the GitHub App, inside warm, Chainguard-hardened microVMs, so every pull request arrives pre-validated.
Enable agents and developers to test, fail, and fix their own code in a fraction of the time by calling CI from within their agent loops for pre-commit checks, delivering fully verified, ready-to-merge changes faster.
Bypass repetitive package downloads and toolchain setups on every run. Start CI from warm snapshots with pre-loaded dependencies, so you can skip straight to execution, shrinking build times and compute costs.
Run CI inside secure-by-default Chainguard microVMs that produce cryptographically signed attestations. Prevent untrusted agent code from breaching host infrastructure, stealing credentials, or faking pipeline results.
WHY CHAINGUARD?
The Chainguard Checks difference
Fast pipeline provisioning
Start CI in seconds using microVM environments pre-loaded with dependencies, eliminating setup friction for developers and AI agents.
Exfiltration-safe by design
CI runners never hold long-lived secrets. Credentials are injected host-side, and workflow steps needing on-disk credentials get short-lived, encrypted stand-ins that are worthless to steal.
No broken PRs with Workspaces
Block unverified PRs automatically. Checks feeds test results directly back to running agents, triggering self-correction before PRs are opened.
Cut merge times and compute
Bypass redundant CI runs. The merge gate can verify the Checks attestation on the PR and merge immediately.
Secure CI environment
Prevent runner compromises. Each workflow step runs in a microVM built with zero-CVE Chainguard OS Packages.
Block untrusted dependencies
Keep unauthorized packages out of your pipeline. Every build dependency is verified against your lockfile before execution.
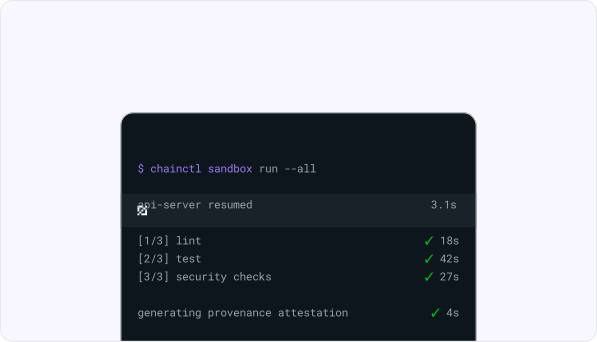
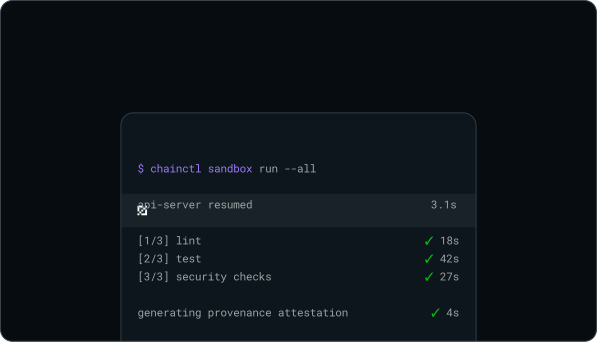
Shift CI left
Eliminate discrepancies between local development and remote pipelines. Spin up identical CI environments in seconds to run checks pre-commit and use passing CI attestations to bypass additional pipeline runs.
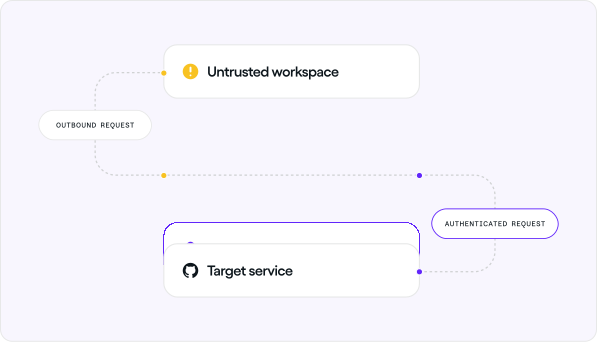
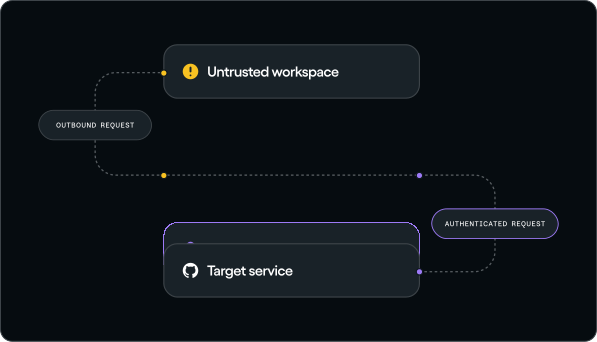
Get secretless pipelines
Run CI safely without exposing long-lived tokens or secrets to untrusted agent code. In-flight host-side credential injection issues short-lived tokens or proxy-injected headers, so there's nothing to steal.
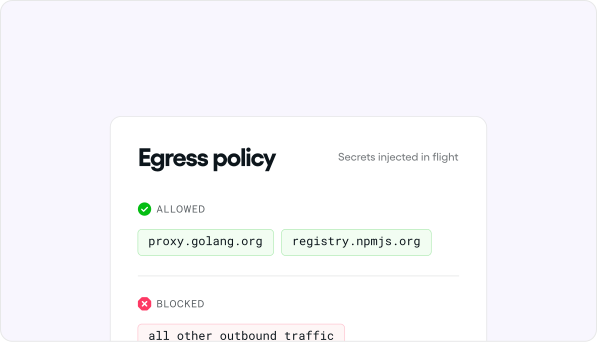
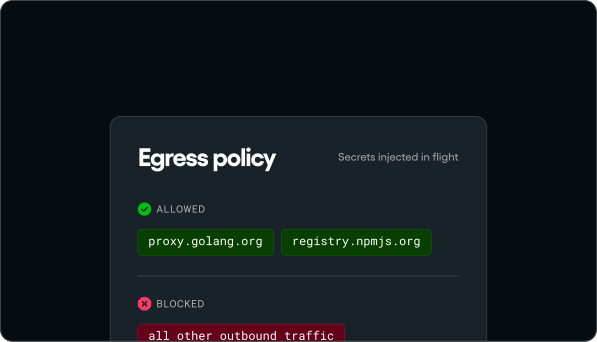
Lock down network egress
Ensure that build and test workflow steps communicate only with what you explicitly allow. Network proxies enforce strict egress rules during CI checks, blocking arbitrary outbound connections.
Trust in every phase of the SDLC
Explore the rest of Chainguard's product suite
Code safely with agents
Build with trusted artifacts
Ship through trusted CI
Chainguard Checks is currently in beta and is a Technology Preview under Chainguard's Master Services and License Agreement.