Chainguard Actions
Prevent compromised actions from becoming your problem
Give developers the freedom to use the actions they want, safely. Get a catalog of 1,000+ drop-in replacements, continuously hardened against credential leaks, script injections, and more.
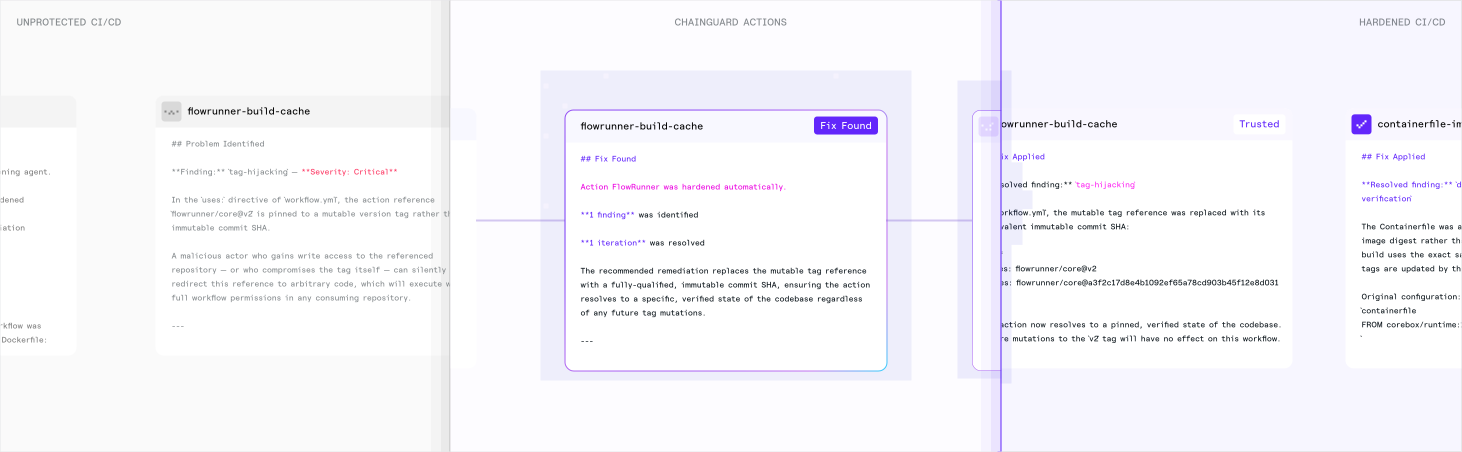
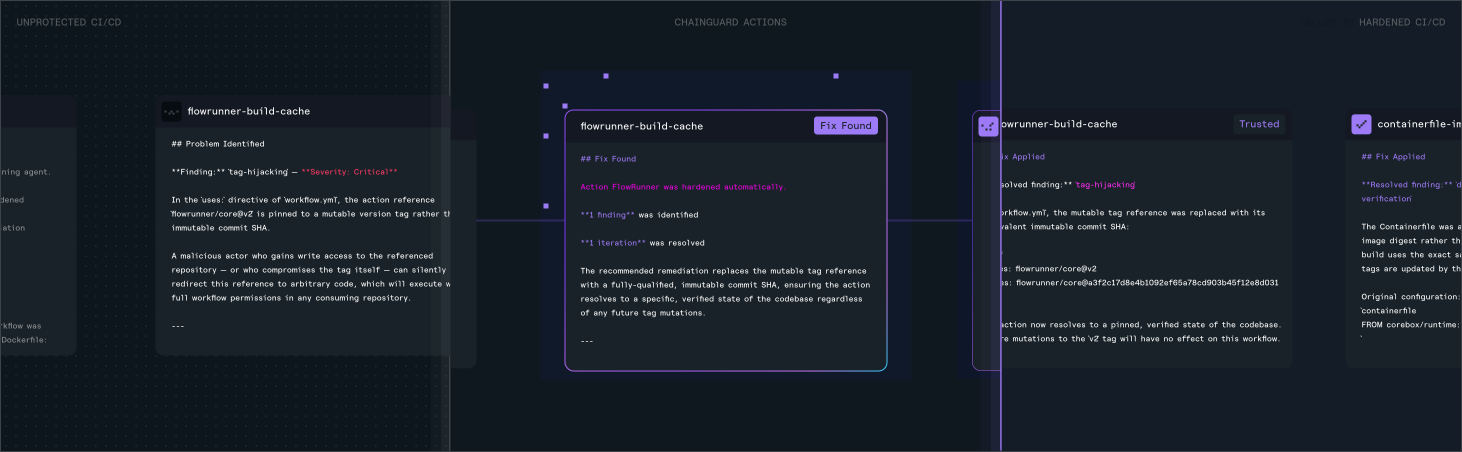
Everything your team needs to trust the actions in your pipelines
Standardize without the toil, stay protected over time, and prove it to anyone who asks, all with a continuously hardened catalog.
Full coverage, fast
Ensure gapless workflow security with a catalog of 1,000+ hardened third-party actions. If a required action or version is missing, request it and have it added, along with all its transitive dependencies, within one business day.
Ongoing peace of mind
Keep your workflows safe from adoption onward. Chainguard re-verifies and rehardens every action whenever its upstream version changes or a new attack pattern emerges.
Prove your pipelines are secure, on demand
Have evidence of how every action was hardened. Every Chainguard Action ships with a full hardening report so you know exactly what was fixed, why, and how.


Jeremy Young
Software Engineer and Security Architect, Xometry
Watch Chainguard harden a popular GitHub Action
See how Chainguard takes a popular Action with a real script injection vulnerability and hardens it into a drop-in replacement that’s safe to run in your workflows.
Fortify your pipelines from common attacks
Attackers won't wait for your next security review. Chainguard Actions continuously secures your CI/CD workflows against known exploits and novel ones before they reach your pipeline.
Attackers retroactively point version tags at malicious commits. Every Chainguard Action is pinned to a verified source.
Malicious actions masquerade as trusted ones. Every Chainguard Action is built from source and then secured, not copy and pasted from the open marketplace.
Untrusted PRs gain privileged workflow access. Chainguard Actions catch and fix configuration vulnerabilities automatically.
Private keys get dumped into public workflow logs. Chainguard Actions blocks runner memory exposure before it reaches your pipeline.
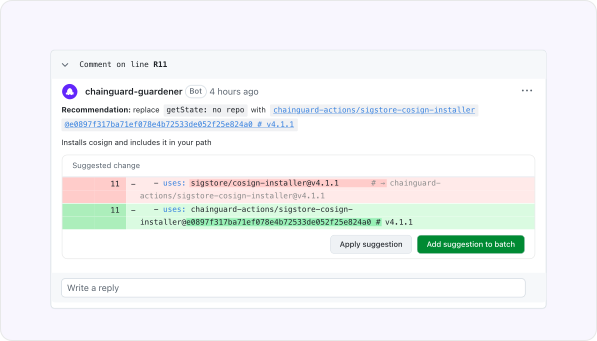
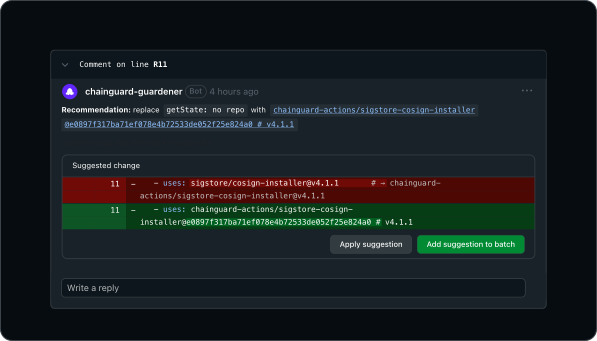
Migrate to hardened actions, fast
Chainguard Actions are drop-in replacements for upstream GitHub Actions. Use the migration skill to migrate one repo at a time, or the Guardener GitHub App for centralized, org-wide rollout.
Trust in every phase of the SDLC
Explore the rest of Chainguard's product suite
Code safely with agents
Build with trusted artifacts
Ship through trusted CI