Point your Go proxy to Chainguard to block malicious dependencies and remediate critical and high-severity CVEs before they ever reach production.






























Multiple layers of security controls protect you from the next malware attack


Malicious behavior scanning
Every package passes through malware and greyware scanning before it's available in our endpoint for consumption.


Configurable cooldowns
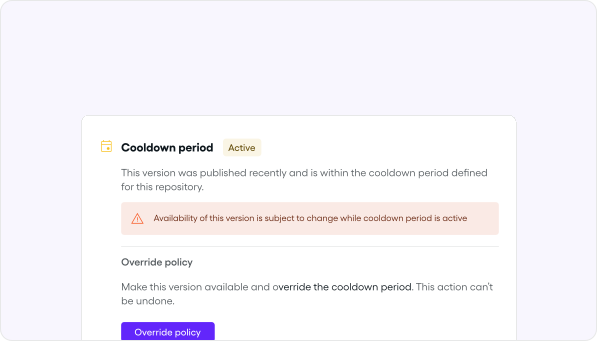
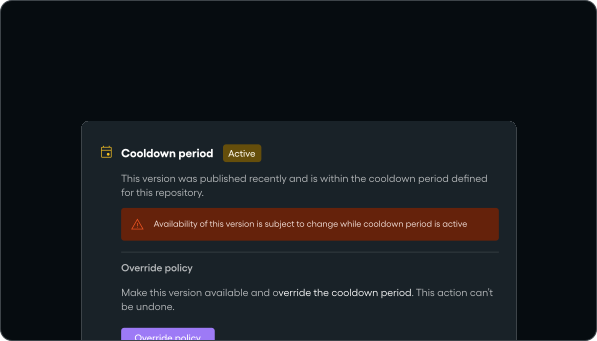
Incorporate a cooldown period of your choosing directly into your Go endpoint to act as a second layer of defense.


Built from source
Popular packages are rebuilt from source to provide another layer of malware protection for hackers' highest value targets.
Step off the CVE remediation treadmill with Chainguard-patched artifacts
Access backported upstream fixes for critical and high CVEs, allowing you to remain secure on your current, stable version while you plan an upgrade.
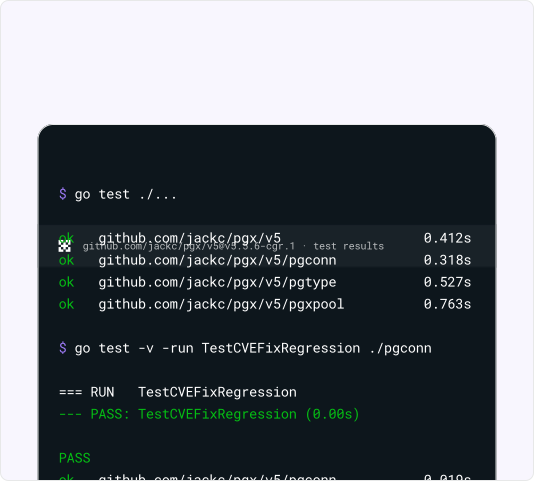
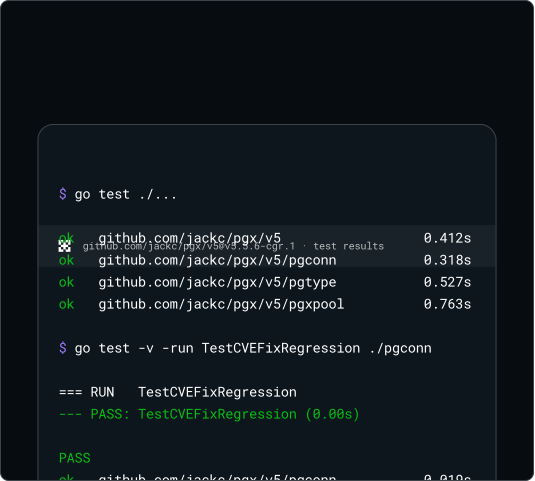
All artifacts are tested to ensure the CVE is fixed while still passing functional tests
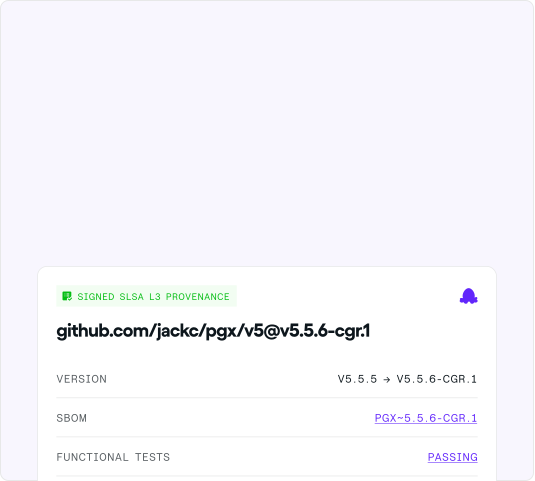
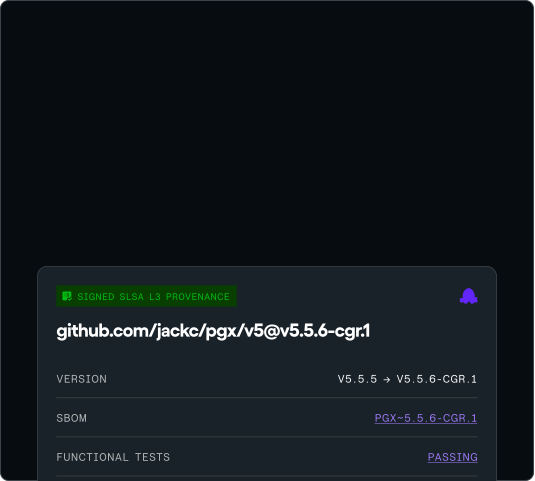
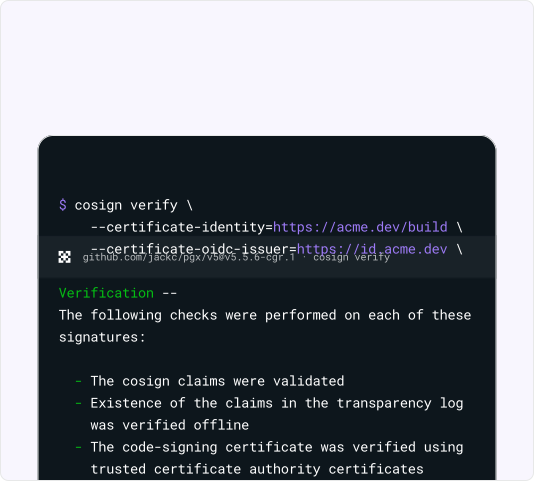
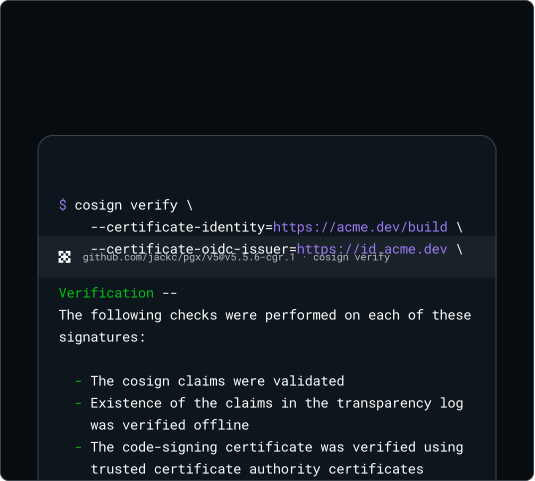
Every remediated artifact ships with signed SLSA L3 provenance and SBOMs
Auditors can run cosign verify to prove artifact integrity
Built for high-velocity engineering teams that can't afford security drag
High-volume tech platforms
Maintain uptime at scale. Secure your Go dependencies to shield massive real-time traffic from supply chain outages.
Fintech and core banking systems
Prevent a compromised package from interrupting a transaction. Protect your mission-critical payment pipelines, gateways, and core banking infrastructure from CVE and malware risk.
Cybersecurity and networking firms
Build security products on secure dependencies. Shield your agents, proxies, and CDN nodes from malicious modules and exploitable CVEs.


Covers all of your Go dependencies
Access the cloud-native infrastructure stack you need, such as gRPC, Kubernetes SDKs, and Prometheus, along with everything else required to build fast, self-contained Go binaries.


Works with your existing tooling
Chainguard Libraries works with your existing artifact managers, scanners, and workflows. Each package has the same functionality as to what you'll find on pkg.go.dev, so there are no breaking changes. Your engineers and agents won't notice a difference.


Signed, sealed, and dependable
Every Chainguard-built version comes with signed provenance and SBOMs inside the artifact metadata, giving you verifiable and auditable proof of integrity.
Govern artifacts based on your compliance standards
Use Chainguard Repository configure policies such as cooldowns, CVE blocking, license restrictions, and more, ensuring every pull abides by your org's unique guidelines.
Learn more about Chainguard RepositoryTrust in every phase of the SDLC
Explore the rest of Chainguard's product suite
Code safely with agents
Build with trusted artifacts
Ship through trusted CI
Chainguard Libraries for Go is currently in early access and is a Technology Preview under Chainguard's Master Services and License Agreement.