Switch your Maven Central registry endpoint to Chainguard Libraries to shrink your CVE backlog and neutralize zero-day threats without breaking changes or forcing lengthy refactors.




























Step off the remediation treadmill with Chainguard-patched artifacts
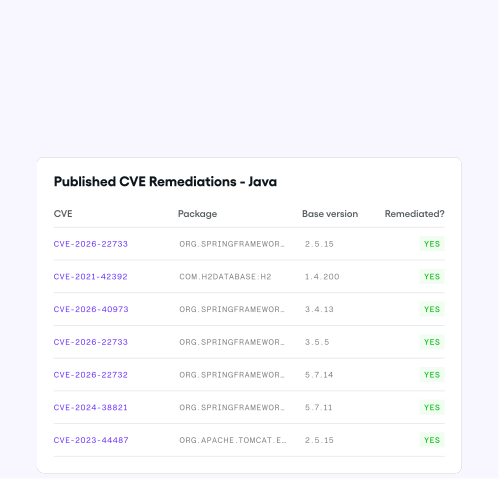
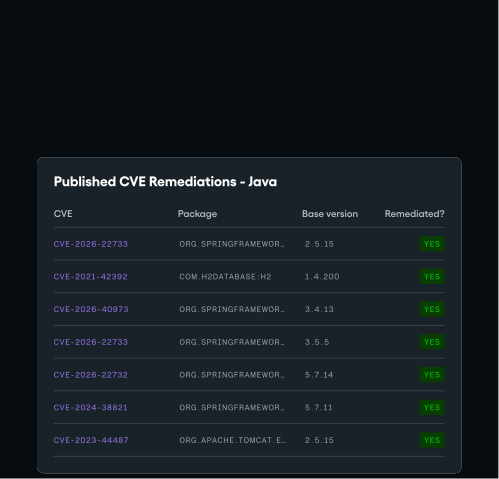
CVE backports for versions you’re stuck on
Fix CVEs in legacy dependencies without forcing version bumps. Every remediated package includes embedded SLSA L3 provenance and SBOMs, letting auditors verify patches with a single CLI command.
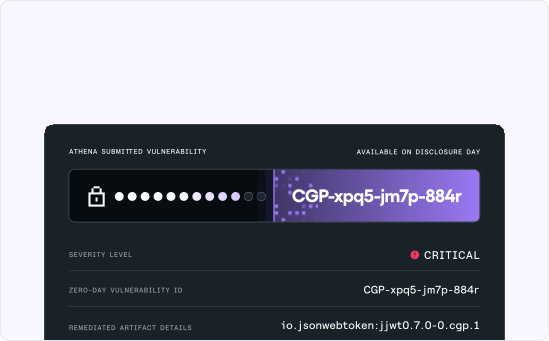
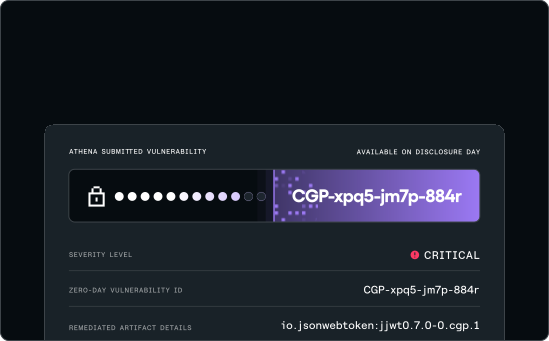
Zero-day protection on day zero, powered by Athena
Benefit from the crowdsourced threat intelligence of the world’s largest institutions. Get day zero access to thousands of packages pre-patched against AI-discovered vulnerabilities, keeping your data safe from hackers.
Built for teams where speed and security are non-negotiable
Financial services
Your transaction processing and fraud detection systems run on Spring Boot and a vulnerable dependency is the last thing standing between you and a security incident that makes the news.
Healthcare and insurance
Your claims processing and patient data systems can’t go down for unplanned upgrades, and backported CVE fixes let you stay compliant with HIPAA and GDPR without rearchitecting your platform.
Enterprise SaaS
Your enterprise customers’ security teams will find every CVE in your stack before you close, so ship with patched Java packages and skip the remediation back-and-forth that stalls deals.
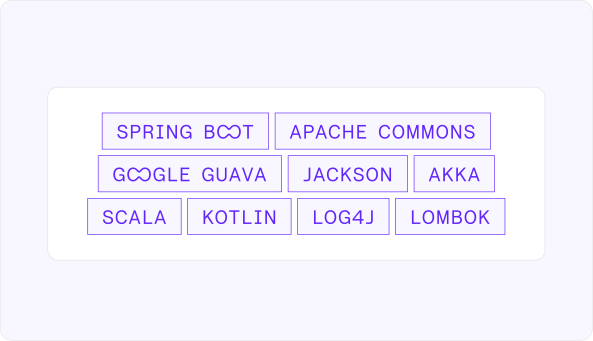
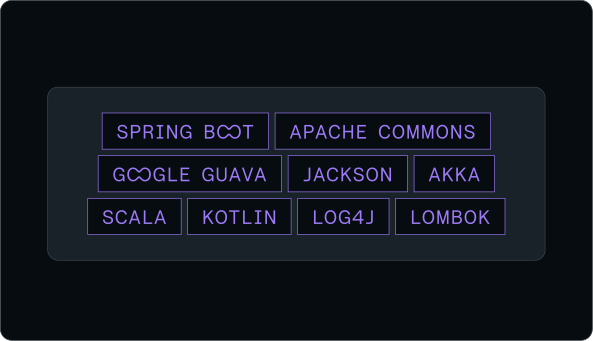
Covers all of your Java dependencies
Access the backend stack you need, such as Spring Boot, Maven, and Hibernate, along with every other dependency your application requires.
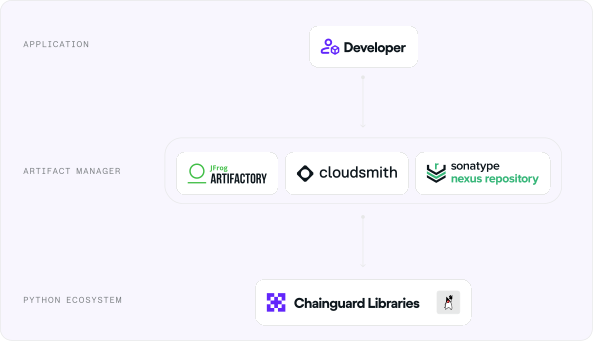
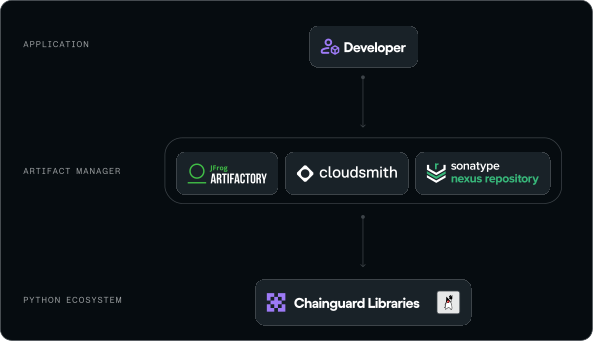
Works with your existing tooling
Chainguard Libraries works with your existing artifact managers, scanners, and workflows. Each package has the same functionality as to what you’ll find on Maven Central, so there are no breaking changes. Your engineers won’t notice a difference.

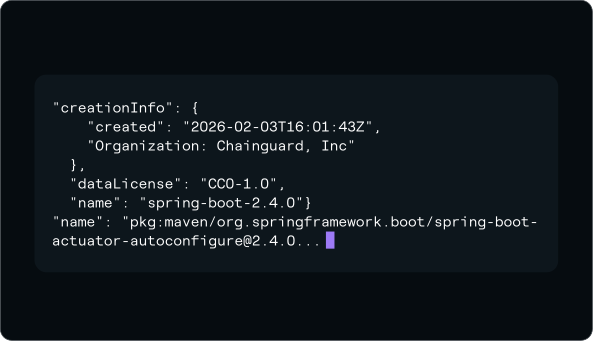
Signed, sealed, and dependable
Every version comes built with full provenance and signed SBOMs, so you have indisputable proof that your dependencies came from the SLSA L3-compliant Chainguard Factory, not a vulnerable maintainer’s machine.
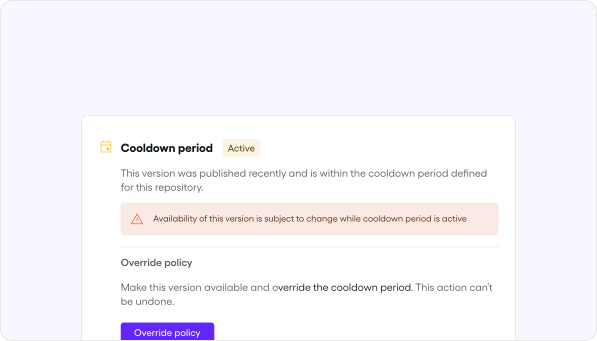
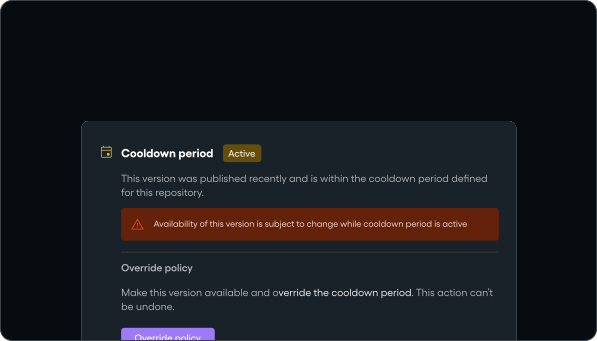
Govern based on your compliance rules
Use Chainguard Repository configure policies such as cooldowns, CVE blocking, license restrictions, and more, ensuring every pull abides by your org’s unique guidelines.
Learn more about Chainguard RepositoryTrust in every phase of the SDLC
Explore the rest of Chainguard's product suite
Code safely with agents
Build with trusted artifacts
Ship through trusted CI