Switch your Python registry endpoint to Chainguard to block malware, patch CVEs, and fix zero-days before AI-assisted attackers can strike.
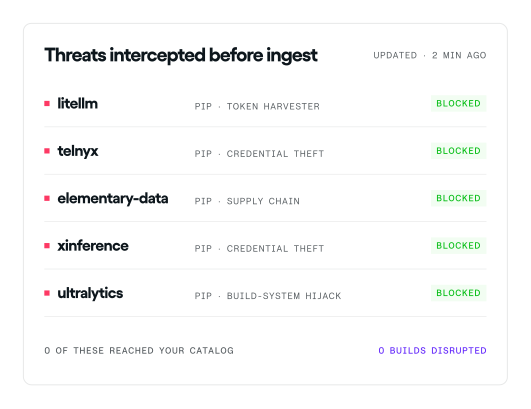




























Multiple layers of security controls protect you from the next malware attack


Malicious behavior scanning
Every package passes through malware and greyware scanning before it’s available in our endpoint for consumption.


Configurable cooldowns
Incorporate a cooldown period of your choosing directly into your Python endpoint to act as a second layer of defense.


Built from source
Popular packages are rebuilt from source to provide another layer of malware protection for hackers’ highest value targets.
Step off the remediation treadmill with Chainguard-patched artifacts
CVE backports for versions you’re stuck on
Fix CVEs in legacy dependencies without forcing version bumps. Every remediated package includes embedded SLSA L3 provenance and SBOMs, letting auditors verify patches with a single CLI command.
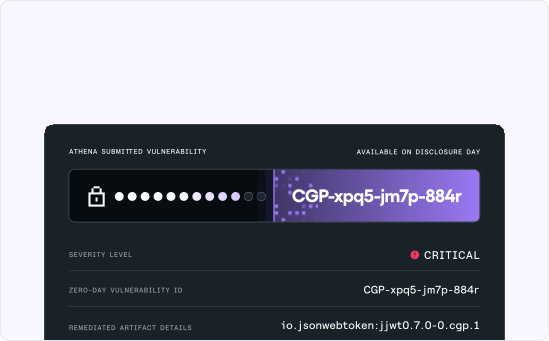
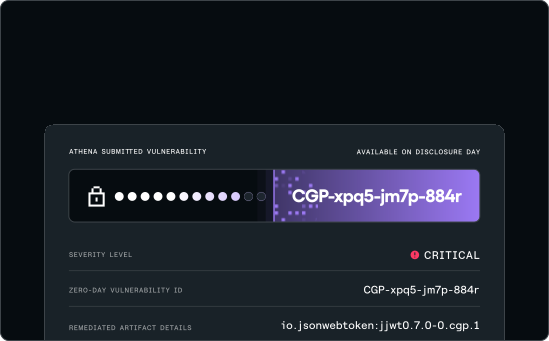
Zero-day protection on day zero, powered by Athena
Access remediated artifacts for zero-day vulnerabilities (silent vulns) the day they’re disclosed. This blocks potential attack paths before bad actors can launch their campaign, keeping your confidential enterprise data safe.
Built for teams where speed and security are non-negotiable
Data teams with legacy apps
End the ‘patch or break’ dilemma. We backport hard-to-fix CVEs, so your production pipelines remain secure while you plan your next major version upgrade.
AI/ML startups
Ship fast with enterprise-grade confidence. Pass customer security reviews on day one by proving your AI stack is built on a secure, malware-resistant foundation.
Highly regulated enterprises
Audit-ready by default. Replace manual audit prep with automation. Signed SBOMs and provenance prove component integrity and simplify compliance evidence reporting.
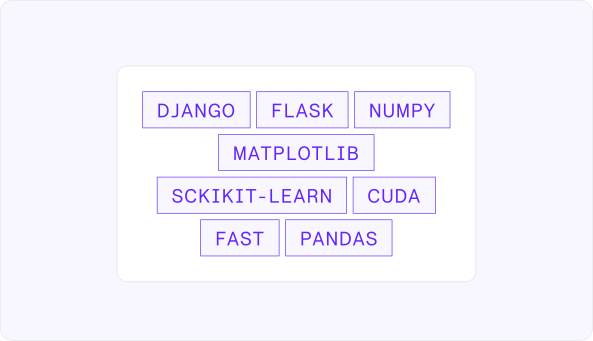
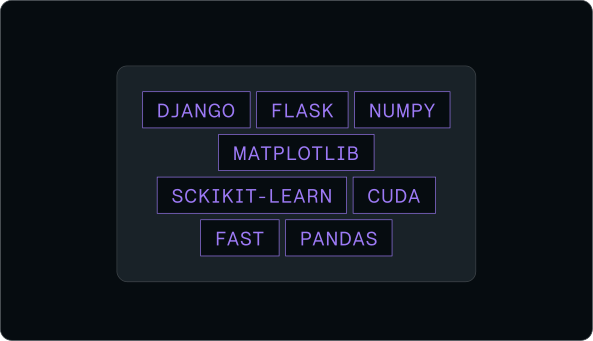
Covers all of your Python dependencies
Access the data science and AI stack you need, such as pandas, numpy, and CUDA, along with everything else you need for your Python application.
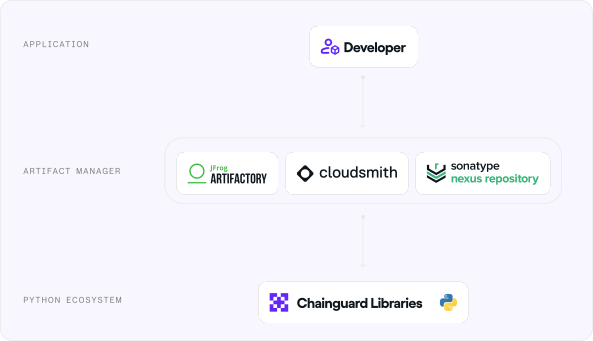
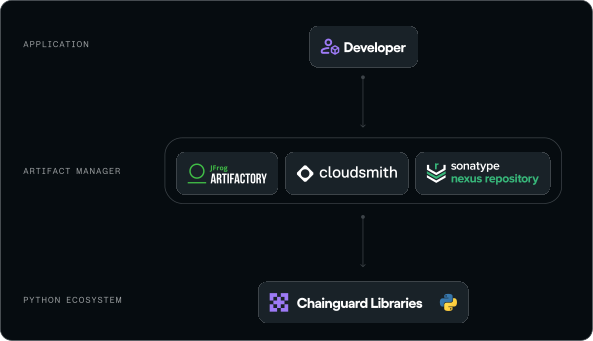
Works with your existing tooling
Chainguard Libraries for Python works with your existing artifact managers and workflows. Each package has the same functionality as to what you’ll find on PyPI, so there are no breaking changes. Your engineers won’t notice a difference.
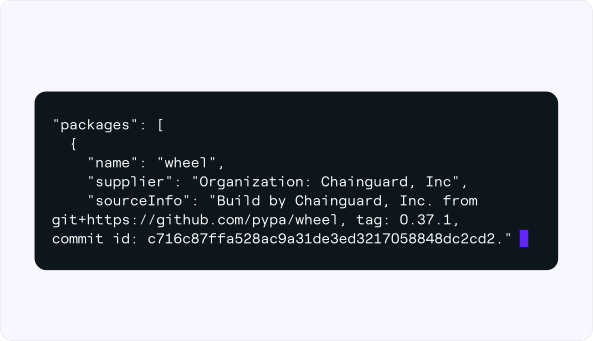
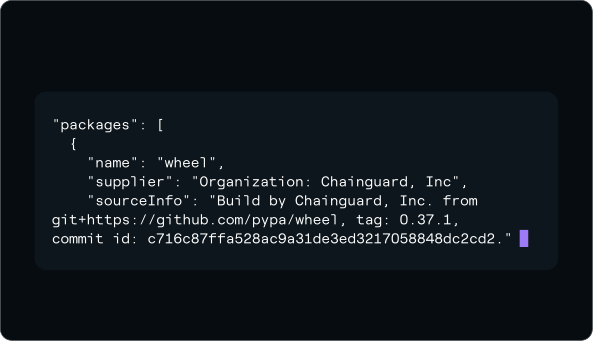
Signed, sealed, and dependable
Every version comes built with full provenance and signed SBOMs, so you have indisputable proof that your dependencies came from the SLSA L3-compliant Chainguard Factory, not a vulnerable maintainer’s machine.
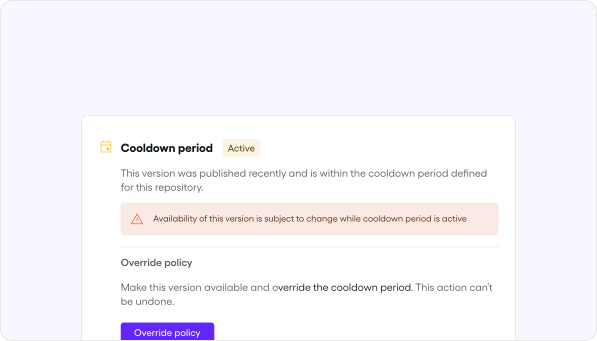
Govern based on your compliance rules
Use Chainguard Repository configure policies such as cooldowns, CVE blocking, license restrictions, and more, ensuring every pull abides by your org’s unique guidelines.
Learn more about Chainguard RepositoryTrust in every phase of the SDLC
Explore the rest of Chainguard's product suite
Code safely with agents
Build with trusted artifacts
Ship through trusted CI
Verwandte Ressourcen
98% less malware: The data behind a safer open source supply chain
Jetzt lesen
This Shit is Hard: The complexities of fixing Python library security issues at scale
Jetzt lesen
This Shit is Hard: Building hardened PyTorch wheels with upstream parity
Jetzt lesen
Introduction to Chainguard Libraries for Python
Jetzt lesen